Criminal investigations increasingly involve digital evidence. Smartphones, computers, cloud accounts, communication platforms, cameras, connected devices and online services can all contain information that helps investigators understand what happened, when it happened and how events may be connected.
The challenge is not simply finding this information. Investigators must collect it appropriately, preserve its integrity, analyse large volumes of data and present relevant findings in a clear and defensible manner.
Law enforcement digital forensics provides the processes and technologies used to identify, preserve, examine, analyse and report digital evidence. When integrated into a structured investigative workflow, it can help turn fragmented digital information into evidence that supports a case.
What Is Law Enforcement Digital Forensics?
Law enforcement digital forensics is the forensic examination of digital devices, systems and data to identify information relevant to an investigation.
Digital evidence can exist on computers, smartphones, storage media, networked systems and other electronic devices. Depending on the source and acquisition method, it may include communications, documents, photographs, application data, browser activity, location information, system records and other digital artefacts.
Digital forensics is therefore relevant to a wide range of investigations, not only cases involving computers or cybercrime.
Why Digital Evidence Matters in Police Investigations
Digital devices can preserve information about activities that may otherwise be difficult to establish. A smartphone may contain communications and location-related information. A computer may contain documents, browser records and application activity. Network environments may contain authentication and connection records, while cloud services may preserve files and account activity.
When examined appropriately, these sources can help investigators determine what happened, when activity occurred, which device or account was involved, what communications took place, how devices or accounts were connected and whether activity from different sources can be placed into a common timeline.
Digital forensics does not automatically establish who performed an action. Findings need to be assessed alongside other investigative evidence and the circumstances of the case.
Types of Digital Evidence Used by Law Enforcement
Mobile Device Evidence
Smartphones combine communications, applications, photography, location-related information and internet access in one device. Depending on the device, condition and lawful acquisition method, investigators may examine messages, application data, contacts, photographs, files, browser information, location artefacts and other available evidence.
Computer and Storage Evidence
Computers and storage devices can contain documents, emails, browser history, application artefacts, system records, metadata and other available information. Examination can help investigators understand what information exists and place relevant activity within a timeline.
Network and System Evidence
Authentication events, connection records, system logs and other network evidence can provide context about activity within an environment. When examined with endpoint evidence, these records may help investigators understand how systems interacted during a particular period.
Cloud and Online Evidence
Cloud storage, online accounts and hosted applications can contain files, account activity and other records that complement evidence from physical devices.
Digital Media and Video
CCTV footage, photographs, audio and other digital media can contribute another layer of evidence. Their timestamps and contextual information may be compared with records from devices or systems to help establish a sequence of events.
The Digital Forensics Investigation Process
1. Identify Relevant Evidence
Investigators determine which devices, accounts, systems or other digital sources may contain information relevant to the investigative question. The assessment should consider the case, available evidence and the legal authority governing collection and examination.
2. Secure and Preserve Evidence
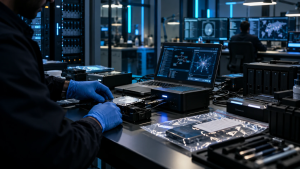
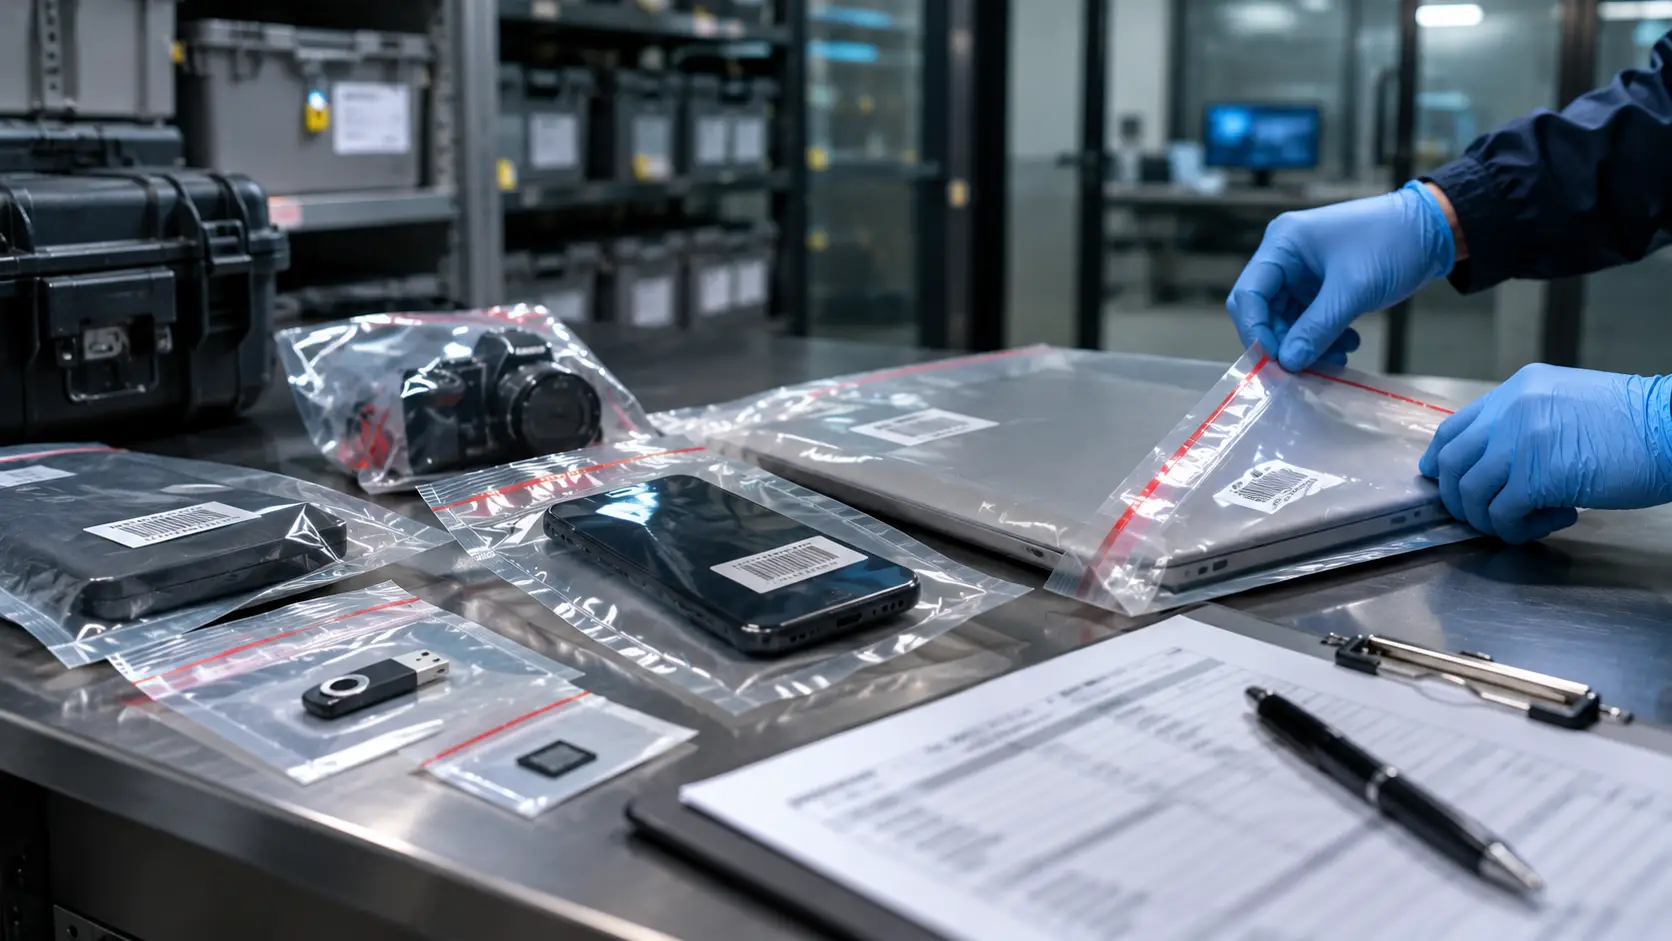
Digital evidence can be altered, damaged or destroyed through improper handling. Investigators therefore need procedures designed to protect the original evidence and document actions taken during seizure, storage, transfer and examination. Where appropriate, forensic examination is performed using a forensic copy rather than the original evidence.
3. Acquire the Digital Evidence
The acquisition method depends on the device, operating system, security state, storage medium and type of evidence required. The objective is to recover relevant information using an appropriate and documented forensic method.
4. Examine and Process the Evidence
Forensic tools can help process and organise acquired information. This may involve parsing application data, examining files, identifying artefacts, recovering relevant information and indexing large datasets for efficient searching.
5. Analyse and Correlate Findings
Investigators can compare timestamps, accounts, device identifiers, communications, locations, files and other attributes to identify relationships between evidence sources.
For example, activity recorded on a smartphone may be compared with computer evidence, network records or other available information. When independent sources support the same sequence of events, they can contribute to a more complete investigative picture.
Pelorus provides digital forensics capabilities covering computers, smartphones, storage media and other digital evidence environments, with evidence correlation supporting investigations that require multiple forensic domains.
6. Document and Report the Findings
A forensic report should explain what was examined, which methods were used, what relevant evidence was identified and how the findings relate to the investigative question. Clear documentation allows authorised stakeholders to understand and review the basis of the findings.
The Role of Digital Forensics Tools
The volume and complexity of digital evidence can make manual examination impractical. Modern digital forensics tools can assist with evidence acquisition, processing, indexing, searching, timeline analysis, artefact identification and reporting.
For law enforcement agencies, the value of a forensic platform goes beyond the number of artefacts it can identify. Agencies should also consider acquisition methods, supported evidence sources, processing performance, reporting, interoperability, security, documentation and how the technology fits into the overall investigative workflow.
Why Evidence Integrity and Chain of Custody Matter
Digital evidence needs appropriate documentation showing how it was handled, transferred and stored. Chain-of-custody procedures help establish the provenance of evidence throughout the relevant stages of an investigation.
Law enforcement agencies therefore need clear policies covering collection, handling and processing. Forensic technology should support these procedures rather than replace them.
Challenges Law Enforcement Agencies Face
Growing Data Volumes
Investigations can involve large quantities of information across multiple devices and platforms. Reviewing every artefact manually can place significant pressure on forensic teams.
Device and Application Diversity
Different operating systems, device models, applications, cloud platforms and data formats can affect what evidence is available and how it can be examined.
Limited Forensic Capacity
Digital forensic laboratories may face more evidence than their teams and infrastructure can process efficiently. This creates a need for scalable workflows and tools that reduce unnecessary manual effort.
Keeping Skills and Technology Current
New devices, applications, operating systems and security mechanisms continually change the digital evidence landscape. Forensic teams therefore need continuing technical training and access to appropriate tools and expertise.
Building a Modern Digital Forensics Capability
A capable digital forensic operation requires more than purchasing forensic software. Law enforcement agencies should consider the complete workflow, including:
- Evidence collection and preservation
- Forensic acquisition
- Mobile and computer examination
- Evidence processing and analysis
- Cross-source correlation
- Secure case and evidence management
- Reporting and documentation
- Investigator and examiner training
- Infrastructure capable of handling growing evidence volumes
- Policies supporting lawful and consistent evidence handling
The technology strategy should also account for how forensic laboratories work with investigators, first responders, legal teams and other stakeholders.
Pelorus’ broader investigation services combine digital forensics with cybersecurity, financial forensics and other investigative capabilities where a case extends beyond a single evidence source.
Digital Forensics and Cyber Investigations
A cyber investigation may include endpoint artefacts, network activity, authentication records, malicious files, online infrastructure and other digital evidence. Analysing these sources together can help investigators understand how an incident occurred and identify evidence relevant to the investigation.
Pelorus’ cybersecurity and threat intelligence capabilities can provide additional investigative context where appropriate.
Conclusion
Law enforcement digital forensics has become an important component of modern investigations. Digital evidence can provide information about communications, devices, accounts, locations, files and activity that may help investigators understand complex cases.
The process requires much more than extracting information. Evidence must be collected appropriately, preserved, examined, analysed, correlated and documented within a structured forensic workflow.
With the right combination of forensic technology, trained personnel and consistent procedures, law enforcement agencies can manage growing digital evidence volumes while producing clearer and more defensible investigative findings.
About Pelorus
Pelorus is a technology company focused on digital forensics, intelligence, surveillance and cybersecurity solutions for governments, law enforcement agencies and organisations conducting complex investigations.
Through specialised technologies and expertise, Pelorus helps investigative teams acquire, analyse, correlate and interpret digital evidence across complex investigative environments.
Strengthen Your Digital Investigation Capability
Digital evidence is becoming central to more investigations, but collecting it is only the beginning. If your agency is evaluating its forensic workflow, evidence processing capability or investigative technology, speak with Pelorus about your requirements.