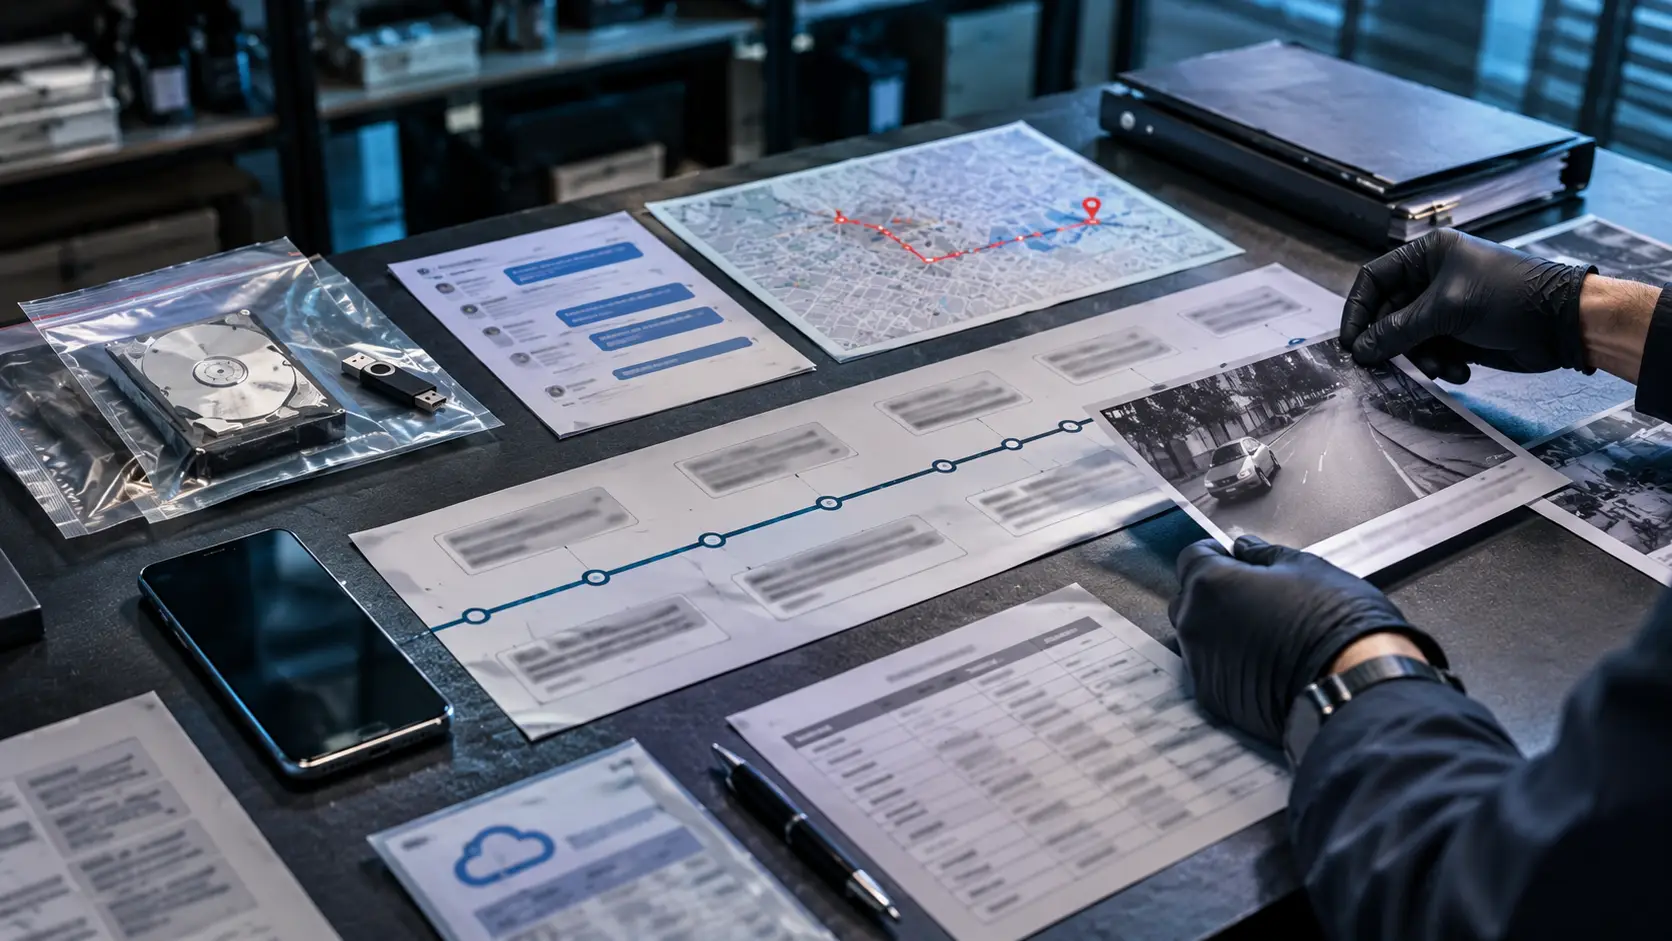
Modern investigations rarely depend on evidence from a single device or system. A smartphone may contain messages and location records, a computer may contain documents and browser activity, network logs may show connections between systems, and cloud accounts may preserve additional activity.
The challenge is not simply collecting this information. Investigators also need to determine how individual pieces of evidence relate to one another.
Digital evidence correlation is the process of examining relationships between evidence from different sources to identify connections, reconstruct events and develop a more complete understanding of an investigation. When performed correctly, it can help investigators move beyond isolated artefacts and establish a coherent sequence of events.
What Is Digital Evidence Correlation?
Digital evidence correlation involves comparing and connecting information recovered from multiple digital sources to determine whether the evidence supports a common event, person, device, location or sequence of activity.
For example, an investigation into suspected unauthorised access may identify a server login, browser activity on an employee laptop, a message on a mobile device and a network connection to an external IP address. Each artefact provides only part of the picture. Examining timestamps, identifiers, accounts, devices and other attributes together may reveal relationships between those events.
This is the fundamental purpose of evidence correlation: connecting individual observations to understand the larger investigative picture.
Why Analysing Evidence in Isolation Can Be Limiting
Digital forensic examinations can produce large volumes of information. Reviewing each source independently may identify relevant artefacts but make relationships harder to recognise.
An examiner might find a deleted document on a computer, a message referencing it on a mobile phone, another copy in a cloud account, a related network connection and a login shortly before the file was accessed. Individually, these findings may appear unrelated. Correlating them can help determine whether they form part of the same sequence of activity.
What Sources Can Be Correlated?
The available sources depend on the investigation, the devices involved and the evidence that can be lawfully acquired.
Mobile Devices
Smartphones can contain communications, application data, photographs, location information, browser activity, contacts and other artefacts. These records can provide timestamps and identifiers that may be compared with evidence from other sources.
Computers and Storage Media
Computers can contain files, browser history, application artefacts, system logs and metadata that provide evidence about activity on a system and when events occurred.
Network Evidence
Network logs and connection records can provide information about communications between systems. When correlated with endpoint activity, they can help establish whether activity observed on a device corresponds with network events.
Cloud and Online Services
Cloud applications and online services can contain files, account activity, access records and other information that complements evidence from physical devices.
Communications and Call Data
Communication records can provide timestamps, participants and other contextual information. When combined with device, location or network evidence, they may help establish relationships between people, devices and events.
Video and Other Digital Media
CCTV footage, photographs, audio recordings and other media can provide another layer of evidence. Their timestamps and contextual information can be compared with records from nearby devices or systems.
How Digital Evidence Correlation Works
1. Define the Investigative Question
Correlation should begin with a clear objective. Investigators may need to determine what happened, when an event occurred, which account or device was involved, how information moved between systems or whether multiple events are connected.
2. Acquire and Preserve Evidence
Relevant evidence must be acquired and preserved using appropriate forensic procedures. Preservation helps protect the integrity of the original evidence, while documentation and chain-of-custody records establish how evidence was handled.
3. Process and Normalise the Data
Different sources may use different formats, timestamps, identifiers and structures. Relevant information may therefore need to be parsed, indexed, normalised and organised before meaningful comparison is possible.
Time zones and timestamp conventions are particularly important. Two systems may represent the same event differently, so investigators need to understand how each source records time.
4. Identify Common Attributes
Investigators can compare attributes such as:
- Timestamps and event sequences
- Usernames and account identifiers
- Device identifiers
- IP addresses and network connections
- File hashes and filenames
- Locations and geolocation data
- Telephone numbers and communication records
- Email addresses
- Application and service activity
A matching attribute does not automatically prove that two events were caused by the same person or system. The strength of a relationship depends on the reliability and context of the underlying evidence.
5. Build Timelines and Relationships
Once relevant relationships have been identified, investigators can reconstruct sequences of activity. A timeline might show when an account was accessed, a file was created, a message was sent and a network connection occurred.
Link analysis can also help identify relationships between people, accounts, devices, locations and events.
6. Validate the Findings
Important findings should be traceable back to the underlying artefact or source. Validation is especially important when conclusions may later need to be explained to legal teams, management, prosecutors or a court.
What Can Evidence Correlation Help Establish?
Reconstructing a Sequence of Events
Correlating timestamps across devices, applications, network activity and other records can help establish the sequence in which events occurred.
Connecting People, Devices and Accounts
Common identifiers can help establish relationships between accounts, devices and individuals, although attribution depends on the evidence available.
Identifying Patterns of Activity
Repeated activity across different sources may reveal patterns that are difficult to recognise when each source is examined separately.
Tracing Digital Information
File metadata, network activity, cloud records and endpoint artefacts can sometimes be correlated to understand how information moved between systems.
Supporting Incident Reconstruction
During a cyber incident, correlation can connect alerts, endpoint artefacts, authentication events, network activity and other evidence to reconstruct what happened.
Digital Evidence Correlation in Cyber Investigations
Cyber investigations often generate evidence across multiple layers of an environment. An endpoint may reveal malware execution, network evidence may show communication with external infrastructure, authentication records may identify the account used, and threat intelligence may provide context about the infrastructure involved.
Correlating these sources can help investigators move from an isolated alert toward a broader understanding of an incident.
Pelorus’ cybersecurity and threat intelligence capabilities include threat intelligence, OSINT, deep web intelligence and dark net monitoring, which can provide additional investigative context when appropriate.
Digital Evidence Correlation in Financial Investigations
Correlation is also relevant to financial investigations. Transaction records, account information, communications, digital devices and other evidence may need to be examined together.
Connecting these datasets can help investigators examine relationships between transactions, entities, communications and digital activity.
Pelorus’ financial forensics capabilities include cross-domain correlation that links financial data with digital, cyber and intelligence evidence.
Challenges in Correlating Digital Evidence
Large Evidence Volumes
Modern investigations can involve large quantities of data from multiple devices and platforms, making manual comparison increasingly difficult.
Different Data Formats
Evidence can arrive as forensic images, application data, logs, cloud records and outputs from different forensic tools.
Inconsistent Timestamps
Time zones, clock settings and timestamp conventions can affect how events should be interpreted.
Duplicate and Overlapping Evidence
The same information may appear in several evidence sources. Investigators need to distinguish genuinely independent corroboration from duplicated records.
Maintaining Evidence Integrity
Correlation must preserve the provenance and integrity of the underlying evidence. Important findings should remain traceable to their original sources.
Human Interpretation
Automated tools can identify relationships, but investigators must determine what those relationships mean within the context of the case. A correlation is not automatically proof of causation or attribution.
How Technology Supports Cross-Source Evidence Analysis
Modern forensic platforms can reduce the manual effort involved in reviewing multiple evidence sources through capabilities such as case management, automated indexing, timeline analysis, link analysis, entity extraction, filtering and visualisation.
Platforms such as Magnet, Cellebrite and Exterro emphasise connecting evidence across devices, communications, cloud environments, logs and other sources rather than forcing investigators to analyse every dataset in isolation.
However, technology should support investigative methodology rather than replace it. Investigators still need to define the question, validate evidence, understand limitations and document how findings were reached.
Why Evidence Correlation Matters for Defensible Investigations
A strong digital investigation is not simply a collection of interesting artefacts. It should provide a structured explanation of what the evidence shows and how individual findings relate to the investigative question.
Cross-source correlation can help investigators test hypotheses against independent evidence, identify inconsistencies and build a clearer chronology. It can also reduce the risk of focusing too heavily on a single artefact when other evidence provides important context.
The goal is not to correlate the largest possible volume of data. It is to establish meaningful, evidence-supported relationships that help answer the question being investigated.
Conclusion
Digital evidence correlation helps investigators connect information that may otherwise remain fragmented across devices, networks, applications, cloud environments, communications and other sources.
Effective correlation starts with a clear investigative question and continues through proper acquisition, preservation, processing, analysis, timeline reconstruction and validation.
When performed systematically, it can help investigators develop a more complete understanding of events while maintaining a clear connection between conclusions and the underlying evidence.
As investigations continue to generate evidence from an increasing number of digital environments, the ability to analyse and correlate those sources will remain an important part of modern digital forensics.
About Pelorus
Pelorus is a technology company focused on digital forensics, intelligence, surveillance and cybersecurity solutions for governments, law enforcement agencies and organisations conducting complex investigations.
Through specialised technologies and expertise, Pelorus helps investigative teams acquire, analyse, correlate and interpret digital evidence across complex investigative environments.
Its capabilities can support evidence-led investigations by helping teams connect information from devices, networks, applications, communications and other digital environments within structured forensic workflows.
Connect the Evidence Behind the Investigation
When evidence is spread across devices, systems, networks and digital platforms, the challenge is understanding how the pieces fit together.